ReliableEvidence is current and the relationship is behaving as expected.
VENDOR INTELLIGENCE
In development
A consistent operating view of third-party risk.
Combine ERP, procurement, contract, compliance, payment, performance, and dependency signals into one explainable vendor profile. Give finance, procurement, operations, and risk teams clear exposure, evidence status, and review actions.
Canonical vendor profiles Trust and dependency separated Source-linked reviews
LIVE
SYSTEM STATUS |
ReviewInspect an evidence gap, meaningful change, or confidence issue.
CriticalAssign an owner where business impact demands faster action.
Third-party operations
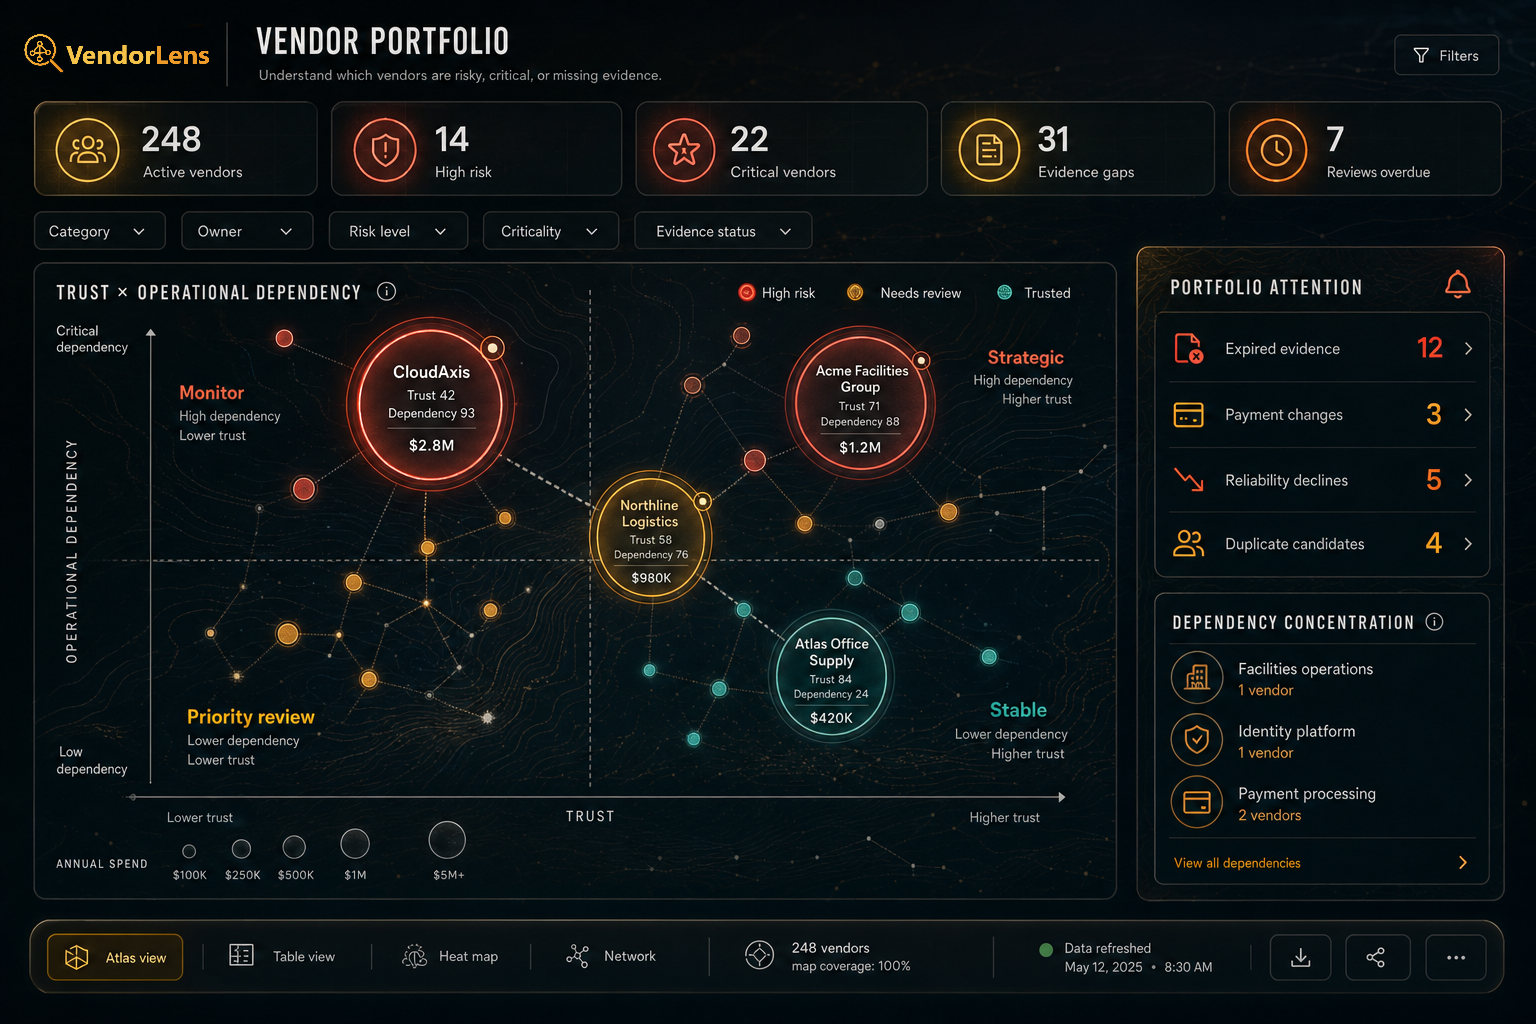
Separate vendor trust, business importance, and evidence readiness.
VendorLens sits beside the systems your team already uses as an intelligence and decision-support layer, prioritizing exceptions without replacing the workflow that owns the action.
ReliableEvidence is current and the relationship is behaving as expected.
ReviewInspect an evidence gap, meaningful change, or confidence issue.
CriticalAssign an owner where business impact demands faster action.
Operating workflow
From fragmented records to a defensible vendor review.
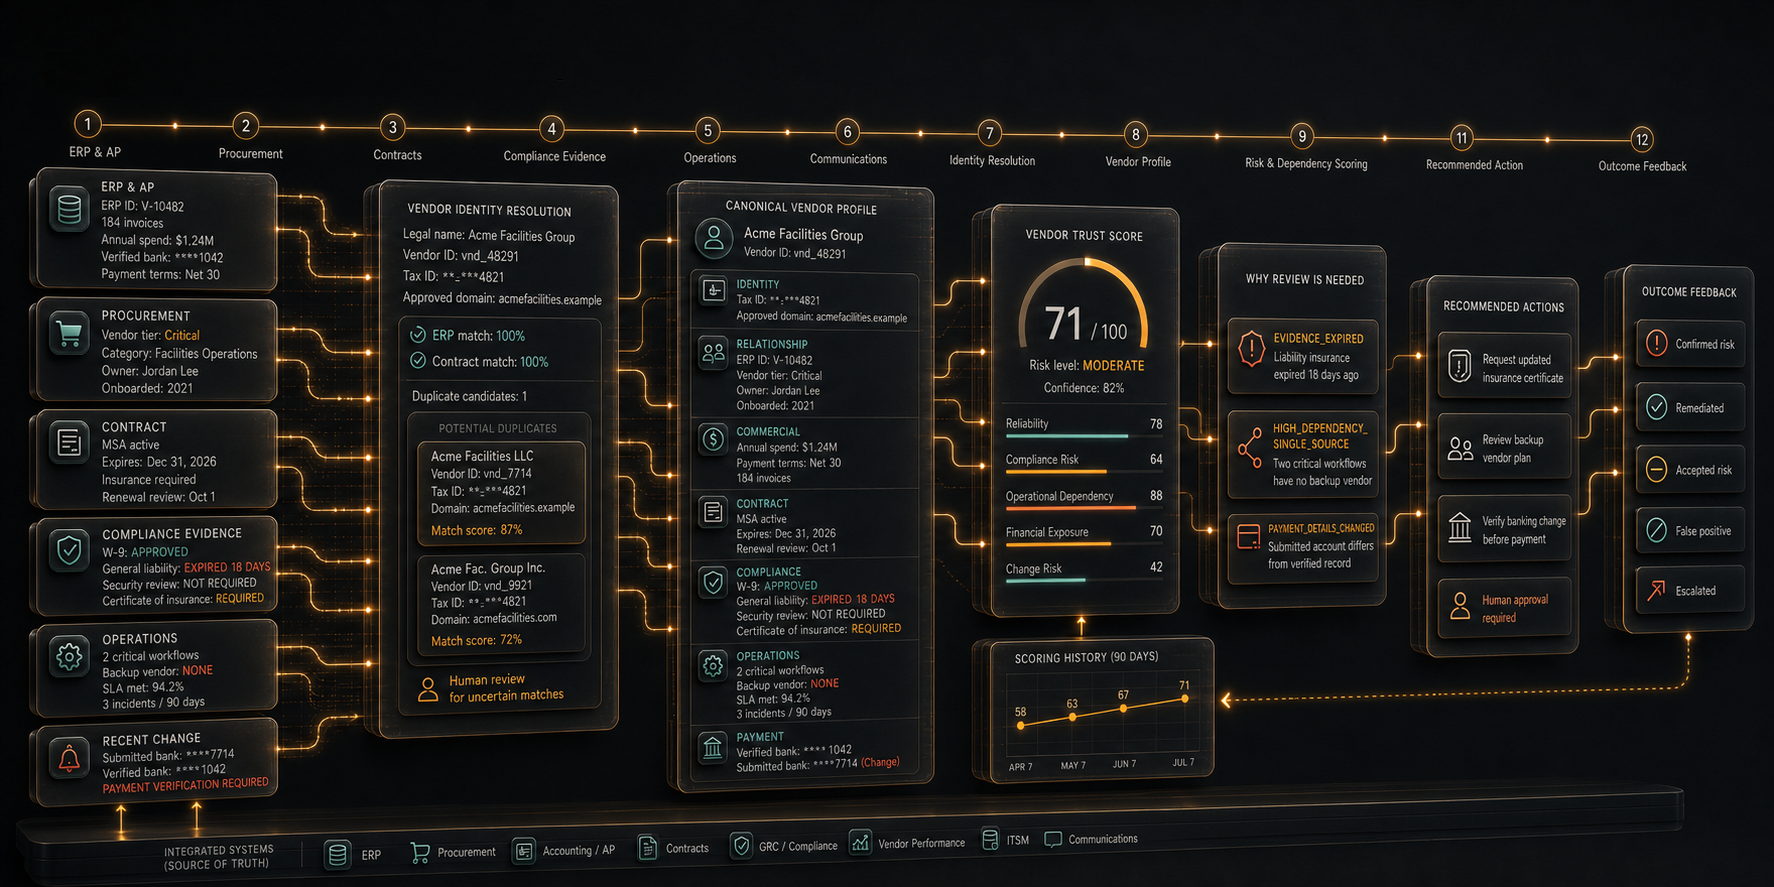
VendorLens resolves duplicate and changing records into a canonical vendor profile, calculates trust and dependency scores, explains what changed, and creates a review plan with source-linked evidence.
LIVE
SYSTEM STATUS |
Resolve
Map aliases, subsidiaries, domains, contacts, and payment references to the correct vendor.
Score
Calculate reliability, compliance, dependency, financial exposure, change risk, and confidence.
Explain
Show reason codes, score deltas, evidence freshness, and the business areas affected.
Review
Assign the right owner, due date, remediation step, and auditable outcome.
Focused capabilities
Start with the vendor changes procurement and operations can act on.
The first release stays focused on explainable vendor intelligence, visible confidence, and manageable review queues instead of becoming another procurement suite.
Reliability and service history
Track incidents, disputes, delivery patterns, SLA performance, escalations, and material changes against the vendor’s own history.
Evidence and compliance readiness
Surface missing, rejected, expiring, expired, waived, or accepted-risk evidence before reviews and audits.
Operational dependency
Map the departments, systems, processes, contracts, and revenue streams that rely on each third party.
Identity and payment changes
Detect duplicate records and meaningful changes to names, domains, contacts, tax details, bank references, and payment instructions.
Portfolio-level exposure
Move from one vendor finding to a third-party governance decision.
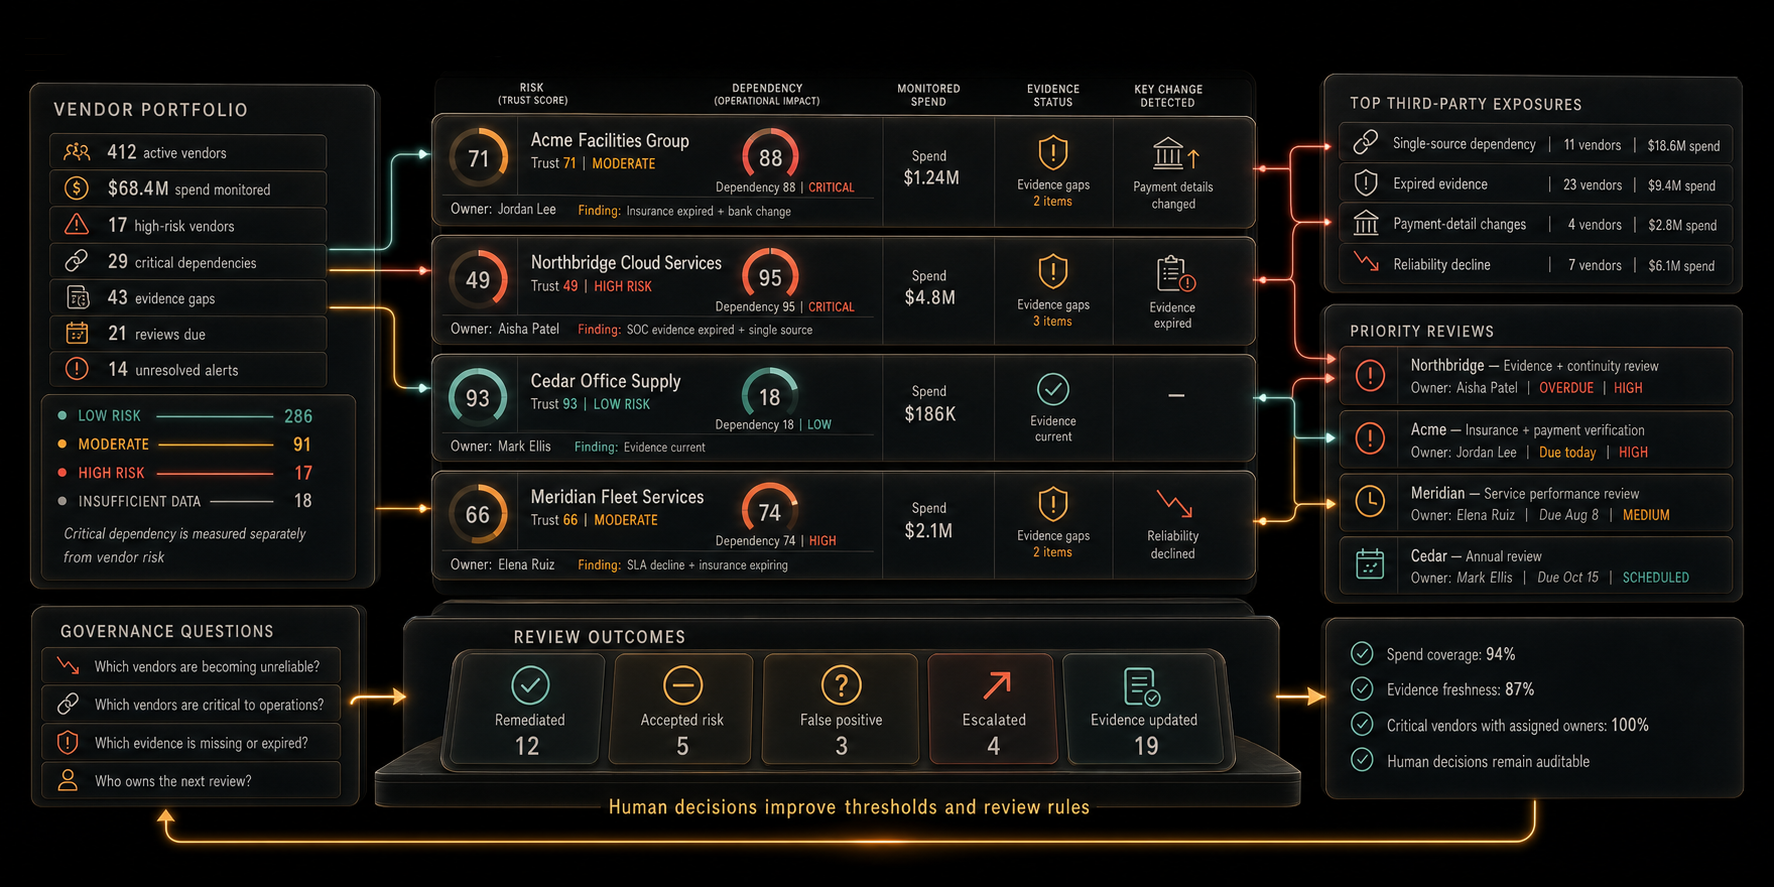
VendorLens connects trust, dependency, spend, evidence status, ownership, key changes, and review outcomes so leaders can see which third-party relationships deserve attention first.
Separate risk from importance
Keep vendor trust, operational dependency, financial exposure, and accepted exceptions as distinct decision inputs.
See evidence readiness
Make missing, expiring, rejected, or waived evidence visible before an audit or renewal.
Prioritize the portfolio
Rank review work by the combination of business impact, material change, and confidence.
VendorLens · Third-Party Exposure
LIVE
SYSTEM STATUS |
Fits the current stack
Bring signals in. Send decisions back where work happens.
VendorLens is designed to complement your current systems. Start with files or APIs, then add connectors and workflow routing as the operating model matures.
Example sources
ERPAccounts payableProcurementContractsGRCCompliance evidence
Decision outputs
Vendor profileTrust scoreDependency scoreEvidence readinessReview plan
Operational flowCustomer-controlled
01
Source systemsRecords, events, documents, and evidence
02
VendorLensResolve, score, explain, and recommend
03
Owned workflowReview queue, application, report, or API action
Governance standard
Useful intelligence without hidden certainty.
VendorLens is designed for decisions that need visible evidence, understandable limits, and accountable human ownership.
Importance is not wrongdoing
A critical vendor is not automatically a bad vendor; dependency and trust remain separate.
Evidence stays legible
Reason codes, source freshness, exceptions, and score changes remain visible to reviewers.
Governance stays human
VendorLens prioritizes and explains; authorized owners make approvals, exceptions, and remediation decisions.
Product roadmap In development
Focused first. Expanded with evidence.
VendorLens is being designed to make third-party risk legible and actionable without silently approving vendors or treating incomplete data as confirmed misconduct.
- CSV and API vendor import with canonical profiles
- Evidence readiness and document lifecycle tracking
- Explainable vendor trust and dependency sub-scores
- Vendor review queue, owners, outcomes, and audit history
- ERP, AP, procurement, contract, and GRC integrations
- Vendor-change detection and stronger duplicate resolution
- Dependency mapping and executive exposure reporting
- Tenant-specific evidence rules, thresholds, and review policies
Product development
Bring a clearer third-party operating view into your governance program.
VendorLens is in development. We are evaluating procurement, finance, accounts-payable, operations, compliance, and third-party-risk requirements against the initial product scope.